In Her Final Weeks, SEC's Peirce Calls for Ending the KYC 'Panopticon'
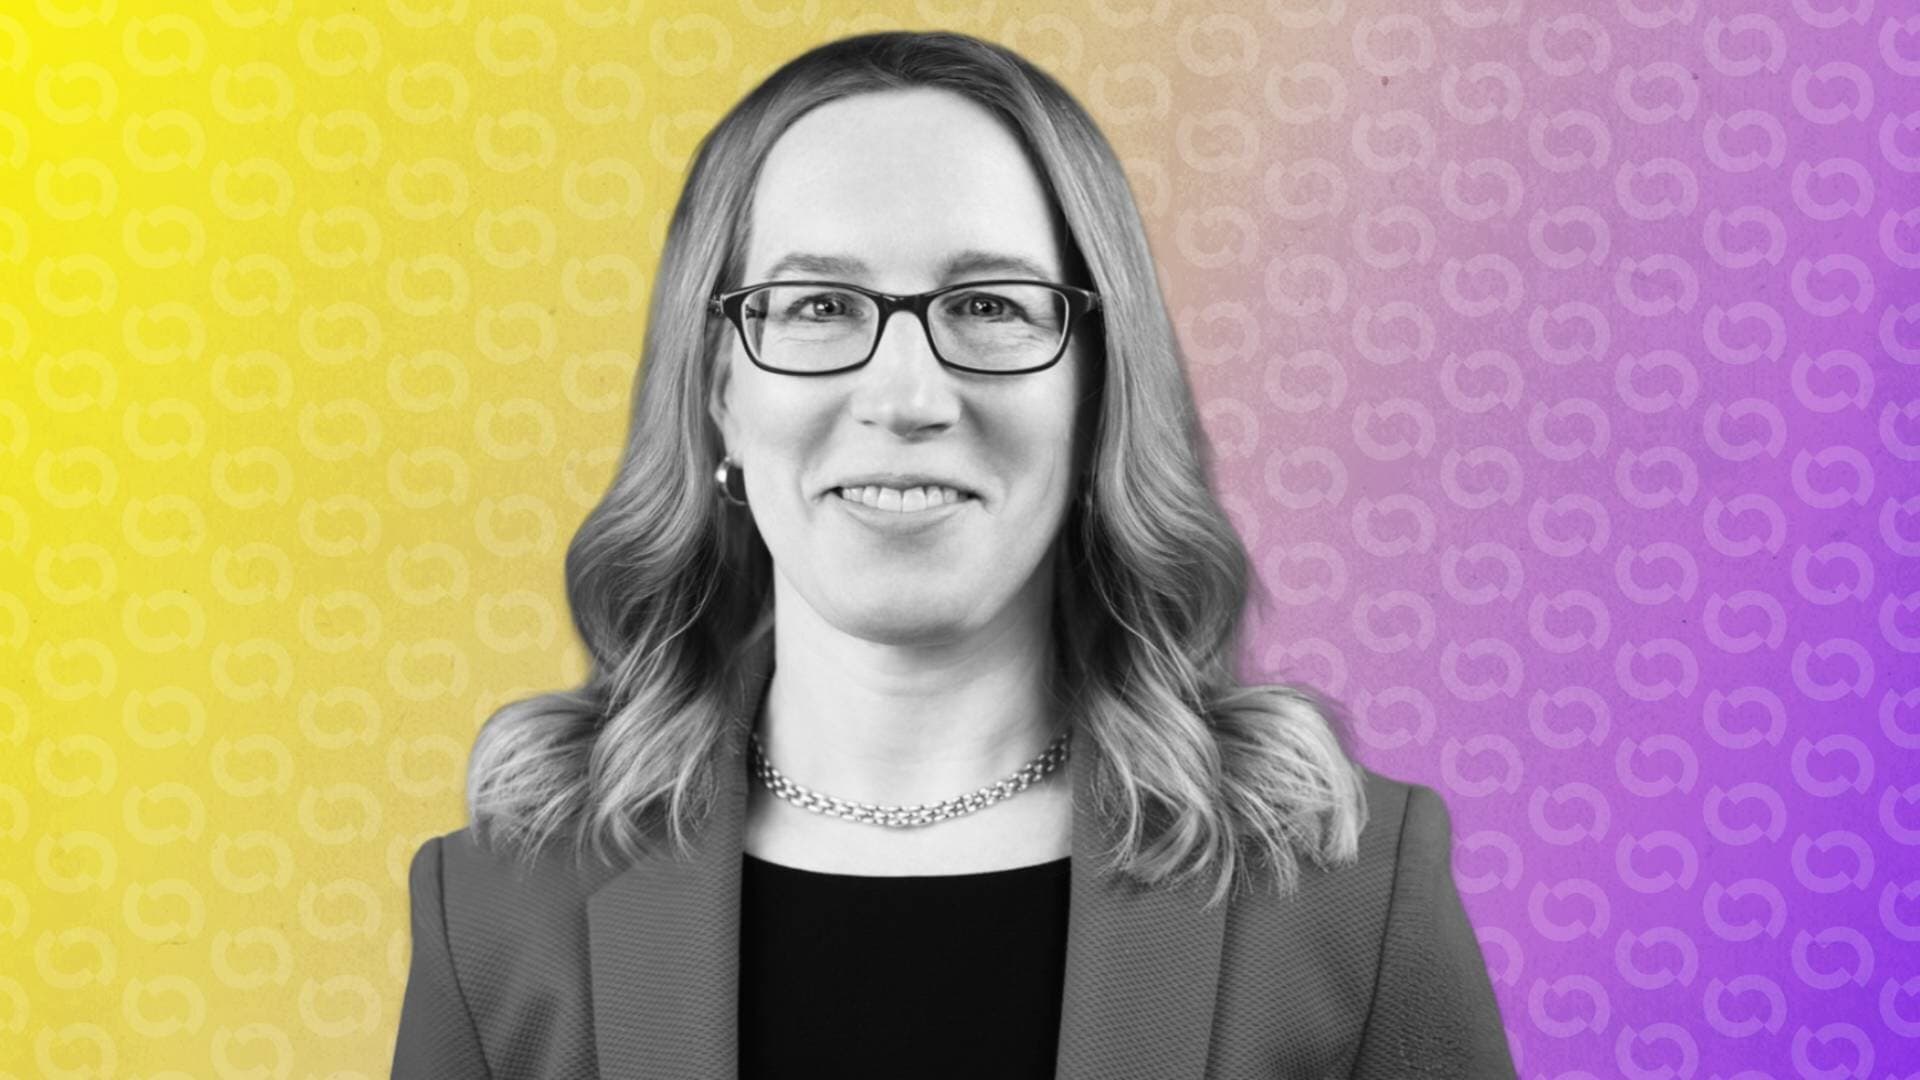
Departing SEC Commissioner Hester Peirce told SIFMA’s Digital Assets Conference that current KYC/AML practices create large, vulnerable repositories of personal data that can be exploited, and urged adoption of cryptographic tools such as zero-knowledge proofs and attribute-based credentials to verify compliance without broad data collection. She warned that continuing to amass customer records risks turning financial systems into surveillance platforms while exposing people to phishing and physical attacks after recent KYC leaks.
Why It Matters
Peirce’s remarks link a technical alternative—privacy-preserving proofs—to concrete security risks highlighted by recent breaches, framing KYC policy as both a privacy and safety issue as she departs the SEC. Given her role as a prominent crypto-friendly regulator, her call could influence debates over how firms and regulators balance identity checks with data minimization.
Key Facts
- Speaker: Hester Peirce, departing SEC Commissioner
- Event: SIFMA's Digital Assets Conference in New York
- Main proposal: Use zero-knowledge proofs and attribute-based credentials to verify attributes without exposing personal data
- Criticism: KYC/AML creates 'ever bigger data haystacks' and a 'panopticon' of surveillance
- Recent incidents cited: Revolut exposed passports and full Bitcoin histories after a fraudulent government data request; Trezor had third-party vendor breaches exposing tens of thousands of customers and enabling phishing attacks
In one of her final public appearances as an SEC commissioner, Hester Peirce argued that current know-your-customer and anti-money-laundering practices are creating oversized, hackable stores of personal data that undermine the protections they aim to provide. Speaking at SIFMA’s Digital Assets Conference in New York, Peirce framed the regime as premised on the idea that collecting more information will help authorities spot criminals, but said the result is increasingly unwieldy "data haystacks" that make needles harder to find. Peirce proposed a technological shift toward privacy-preserving verification. She highlighted zero-knowledge proofs—cryptographic methods that can confirm a fact without revealing the underlying information—and attribute-based credentials as tools that would let a person prove they meet regulatory requirements (for example, age or sanctions status) without handing over names, incomes, or addresses. She urged regulators to create a framework that encourages these approaches rather than imposing broader data collection. The commissioner tied her recommendations to recent high-profile data incidents. She cited a Revolut breach in which customers’ passports and complete Bitcoin transaction histories were exposed after the company responded to a fraudulent government data request, and a breach at a third-party vendor used by hardware-wallet maker Trezor that revealed tens of thousands of customers and led to phishing campaigns. Those events, Peirce said, increase the danger of "wrench attacks" in which exposed identities and holdings are used to target individuals physically. Peirce also criticized what she called "data maximalists" and suggested regulators allow firms to rely on trusted third-party identity verification services instead of each institution independently copying and storing the same sensitive records across many entities. She noted the remarks were delivered during her "penultimate week" as commissioner, underscoring the speech as part of her closing arguments on crypto policy and regulatory design.
Keep Reading
Bitget confirms $352M security breach, suspends withdrawals
Fed proposes new capital, redemption rules for stablecoin issuers
Ethereum Draft Proposes Compliance Controls for Confidential RWA Tokens
Asia dominates Crypto Adoption Index, Bitget’s $352M hack: Asia Express
Original source: Decrypt